Research — Pwn2Own
$1.26 Million for 98 Zero-Days: Pwn2Own Ireland 2026 Closes With Pixel 10 and Galaxy S26 Compromised
Ikotas Labs took Master of Pwn with $361,000 after a $300,000 Pixel 10 exploit chain on day three. Apple’s iPhone 17 was eligible but saw no attempts — and vendors now have 90 days to ship patches before the Zero Day Initiative discloses.
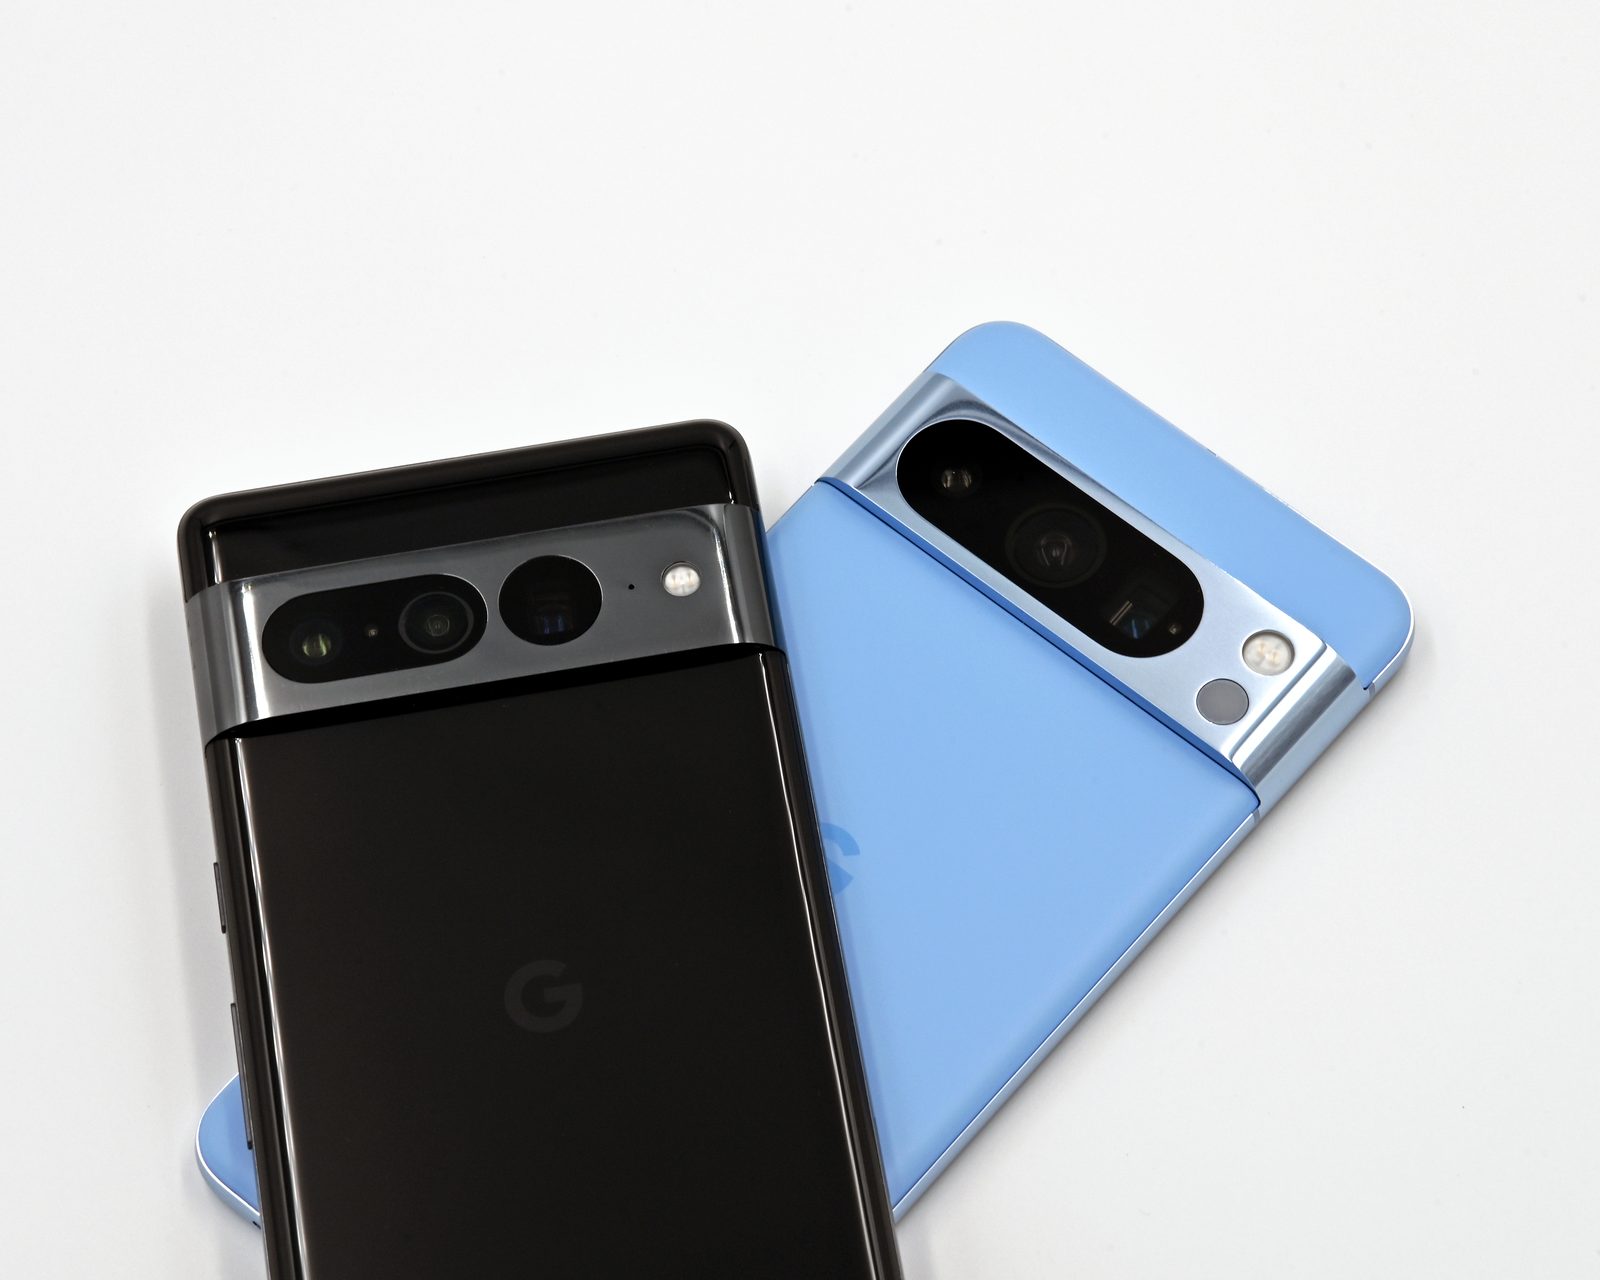
Photo: SimonWaldherr, CC BY-SA 4.0, via Wikimedia Commons
Pwn2Own Ireland 2026 concluded in Cork on Oct. 8 with $1,262,000 in rewards paid for 98 unique zero-day vulnerabilities across 61 completed attempts by 29 research teams (final results), organized by Trend Micro’s Zero Day Initiative (ZDI).
Ikotas Labs won Master of Pwn with 42.5 points and $361,000, after hacking the Samsung Galaxy S26, OpenAI Codex, and the Oracle Autonomous AI Database — and claiming the competition’s top $300,000 reward on day three for chaining multiple zero-days to hack the Google Pixel 10. In total, Google’s Pixel 10 was exploited three times on the final day, earning a combined $562,500.
Second place went to Xint with $240,000 and 27.5 points; third went to Team ZyGoat with $125,000 and 27.5 points.
The email that ran code on a Galaxy S26
The most striking single demonstration belonged to Ikotas as well: the team remotely ran code on the Galaxy S26 using a single email, chaining four vulnerabilities — one of which Samsung already knew about — earning an $11,000 bounty. Ikotas CEO Satoki Tsuji described it as “a zero-day that allows RCE [remote code execution] on the latest versions of Google Pixel 10 (probably works on 11 too) and Samsung Galaxy S26 with just sending 1 email.” On X, the team added: “We have successfully executed remote code on the Samsung Galaxy S26.”
Photo: X-SHLIED, CC BY-SA 4.0, via Wikimedia Commons
How the week unfolded
Day one set the pace: Interrupt Labs, Ikotas Labs, and Nguyen Thanh Dat of Viettel Cyber Security hacked the Galaxy S26, some with bugs already known to the vendor, for 32 zero-days and $388,500. Day two brought $232,500 for 45 unique zero-days, with the Galaxy S26 falling three more times — to PetoWorks, Kyeongmin Kim of the KAIST Hacking Lab, and Dimitrios Valsamaras, Ken Gannon, and Tenia Valsamara of CENSUS Labs. White Noise Club (Mikhail Evdokimov, Polina Smirnova, Mate Zombor) attempted the Pixel 10 but ran out of time.
Notably absent from the leaderboard: Apple’s iPhone 17, which was an eligible target with a $300,000 maximum bounty for a remote hack, but for which no contestant registered an attempt.
What happens next
Per-vulnerability details stay embargoed until vendors patch, under ZDI’s 90-day disclosure policy: vendors have 90 days to release security updates before ZDI publicly discloses. Some exploited bugs were already known to vendors, and partial collisions can affect bounty payouts.
No CVE IDs have been assigned or disclosed yet, and no vendor patches were available at the time of reporting.
Corrections: No corrections have been published for this article. (Early reports cited a $232,500 day-two figure; the final totals are $1,262,000 and 98 zero-days.)
Related coverage
About the author
Research worth reading
Get HackedWire’s vulnerability and research coverage in your inbox. Subscribe to the newsletter →