Companies — Policy
Four More States Sue TP-Link Over Router Security and China Ties
Florida, Iowa, Montana, and Nebraska filed consumer-protection suits on Oct. 6, joining Texas in alleging the router maker misled buyers about security and its separation from China. TP-Link denies the claims — and a day later, 21 attorneys general wrote to the FCC.
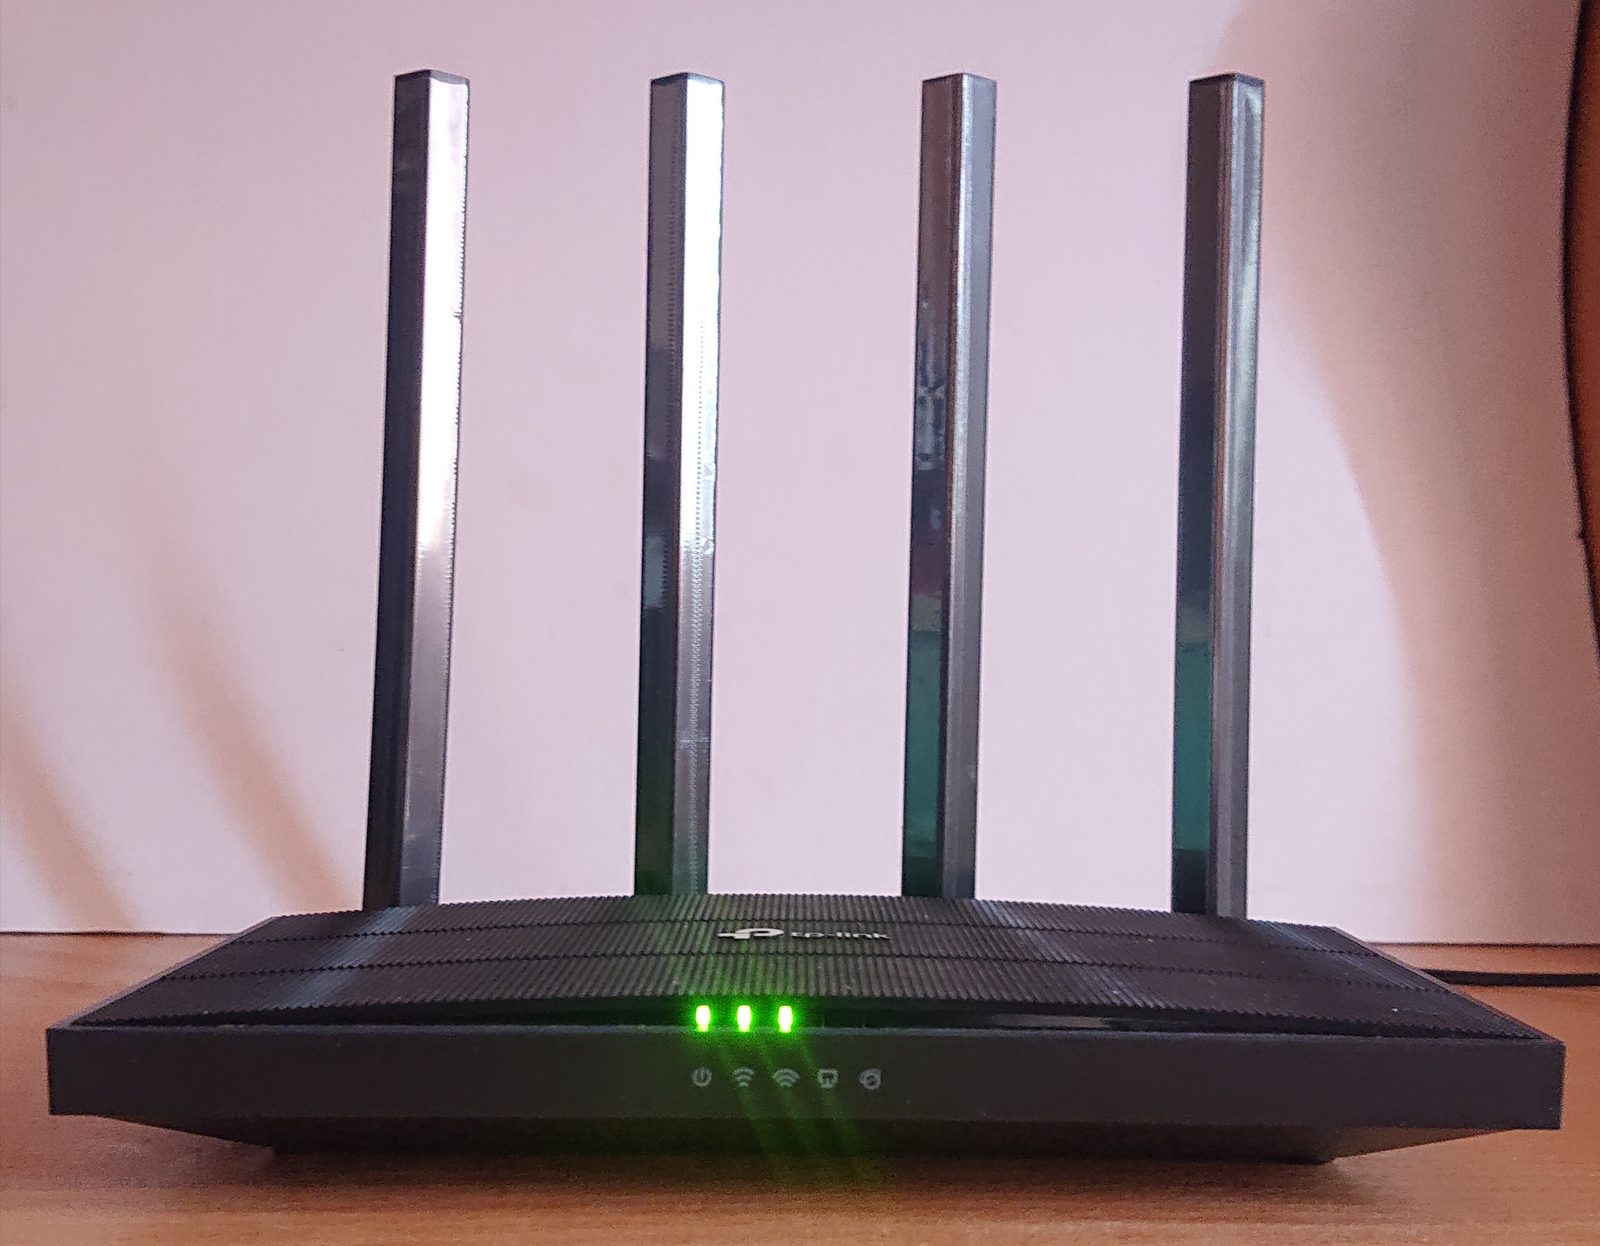
Photo: Paowee, CC BY-SA 4.0, via Wikimedia Commons
Four U.S. states — Florida, Iowa, Montana, and Nebraska — sued TP-Link Systems on Oct. 6 (The Hacker News), bringing the total to five after Texas filed in February. The suits allege the company misled buyers about its routers’ security and about its separation from China. TP-Link denies the claims and says it will fight them in court.
TP-Link Systems is based in Irvine, California. Until a 2024 restructuring, it was affiliated with TP-Link Technologies, a Chinese company the suits do not name as a defendant.
The attorneys general behind the suits are James Uthmeier of Florida, Brenna Bird of Iowa, Mike Hilgers of Nebraska, and Austin Knudsen of Montana. Each suit relies on its state’s consumer protection laws and seeks injunctions, civil penalties, and restitution.
Announcing the Florida suit, Uthmeier said: “Today, we sued TP-Link for lying about the safety of its routers and its ties to the CCP.” He also described “Chinese state-sponsored hackers exploited TP-Link routers sitting in American living rooms.”
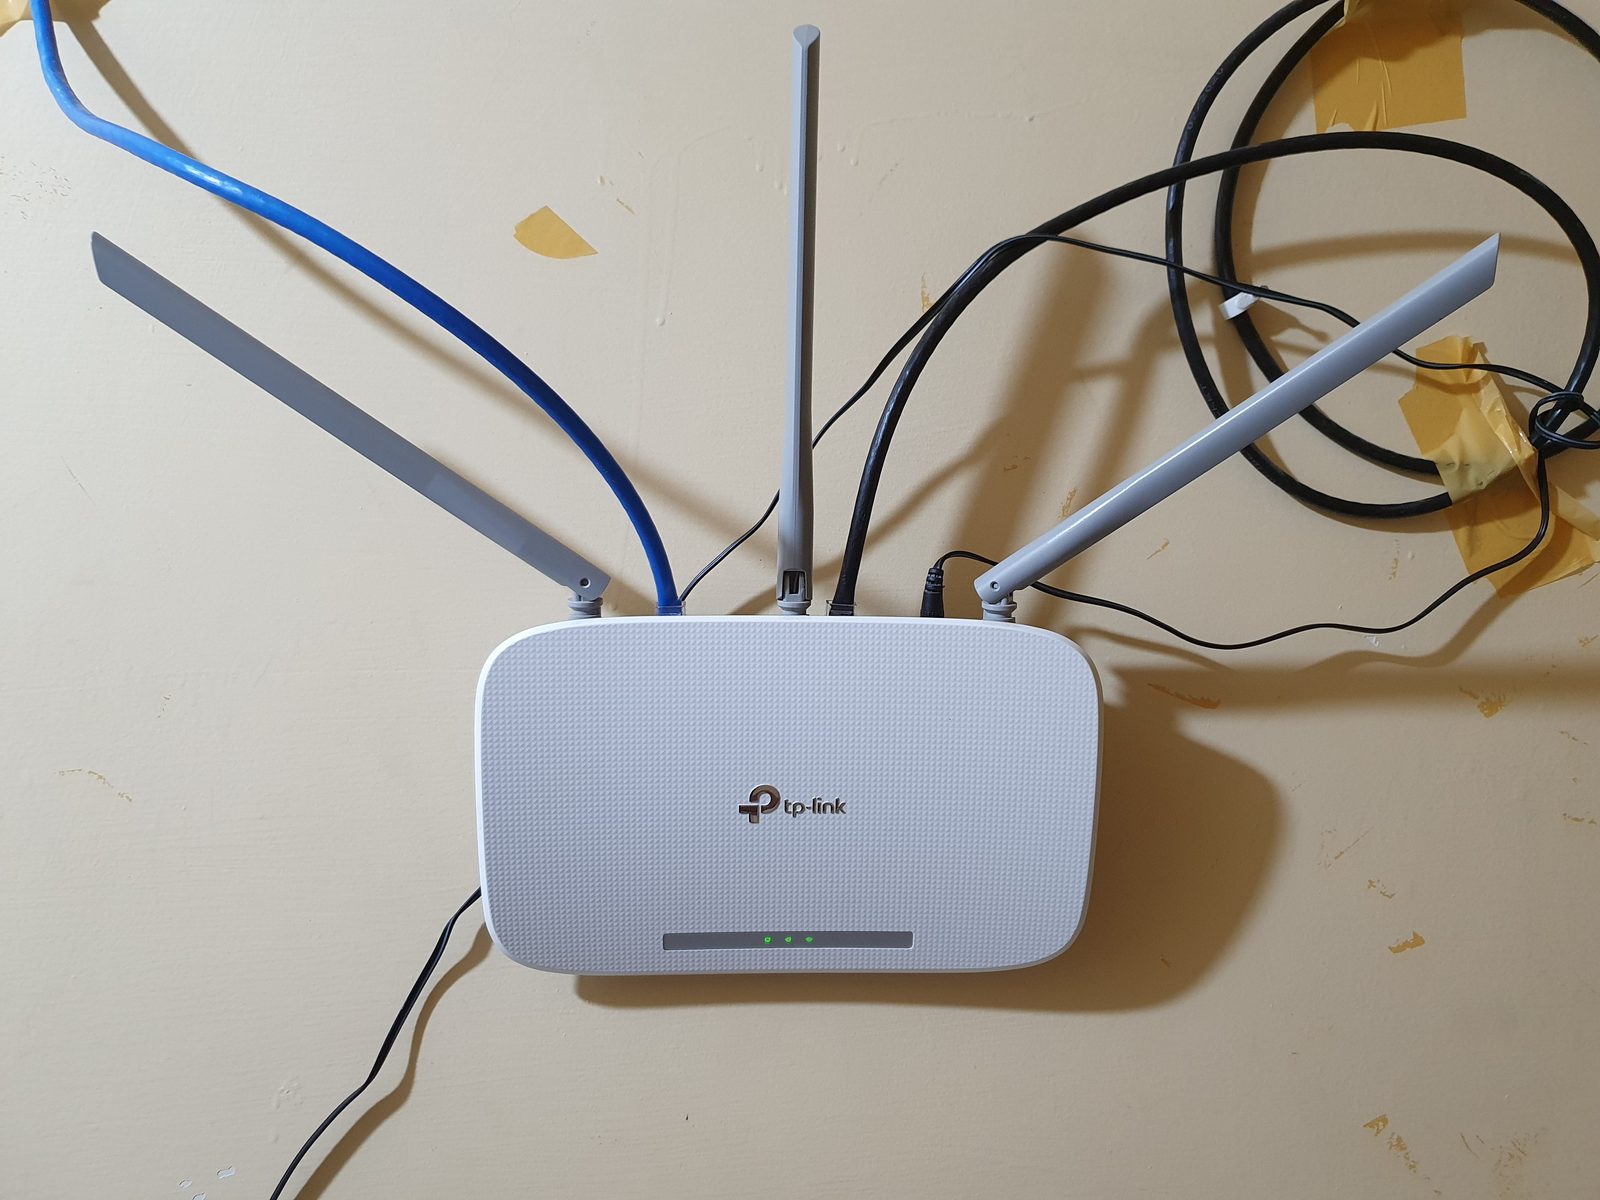
Photo: Kskhh, CC BY-SA 4.0, via Wikimedia Commons
What the complaints actually allege
The complaints cite congressional testimony that TP-Link routers were exploited in the Volt Typhoon and Flax Typhoon campaigns — botnets used by Chinese threat actors for password-spray attacks — and by Russian hackers targeting TP-Link routers. But none of the states allege the Chinese government actually obtained customers’ data through TP-Link: the complaints from Florida, Montana, and Nebraska describe it as a risk under Chinese law, and Iowa’s announcement, while worded more strongly, still frames access as something that could happen.
The suits also challenge TP-Link’s marketing claims, including the HomeShield promise that it “covers all security scenarios” and — as recently as November 2025 — a “100% safeguard” offer. Nebraska’s complaint, per USA Herald’s review of the filing, cites CVE-2023-50224, CVE-2023-1389, CVE-2025-30237, and CVE-2026-9254 as security failures — those are the complaint’s allegations, not independent confirmation of the flaws.
The complaint adds that only 0.5% of the components used at TP-Link’s Vietnam factory, by value, are bought in Vietnam, with all other inputs imported “from or through China.”
The market at stake
TP-Link is not a niche vendor. Circana statistics cited in reporting put the company at roughly 36.6% of U.S. router unit market share and 31% by dollars in 2024. The day after the suits were filed, 21 state attorneys general wrote to the Federal Communications Commission about TP-Link’s bid for approval of new router models — a public letter, not an enforcement action, but a signal that the scrutiny is widening beyond the courtroom.
What remains unknown
- The allegations are unproven; TP-Link denies them and will contest the suits in court.
- No state alleges Chinese government access to customer data actually occurred — the claims are risk-based, and Iowa’s stronger framing is still conditional.
- More states could join: “four more states” is current as of Oct. 6.
- There has been no CISA or FCC enforcement action against TP-Link.
What consumers can do
Regardless of how the litigation resolves, router owners can reduce their own exposure: keep router firmware updated, replace routers the vendor no longer supports with security updates, change default admin credentials, and disable remote administration unless it is actually needed. TP-Link also faces new scrutiny over vulnerabilities in ISP-provided routers, per SecurityWeek — a separate line of pressure worth watching alongside the state suits.
Corrections: No corrections have been published for this article.
Related coverage
About the author
Never miss a policy fight
Get HackedWire’s enterprise and policy coverage in your inbox. Subscribe to the newsletter →